Azure SSO
Finding Metadata in Azure for SSO Configuration
Introduction
This document provides step-by-step instructions on where to locate the metadata in Microsoft Azure when configuring Single Sign-On (SSO) for a new software integration.
Prerequisites
- Administrator access to your Azure portal
- The application must be registered in Azure Enterprise Applications
Easiest SSO Setup Is With A Metadata URL
Finding this link will allow you to simply copy and paste the url and you can rely on us to do the rest!
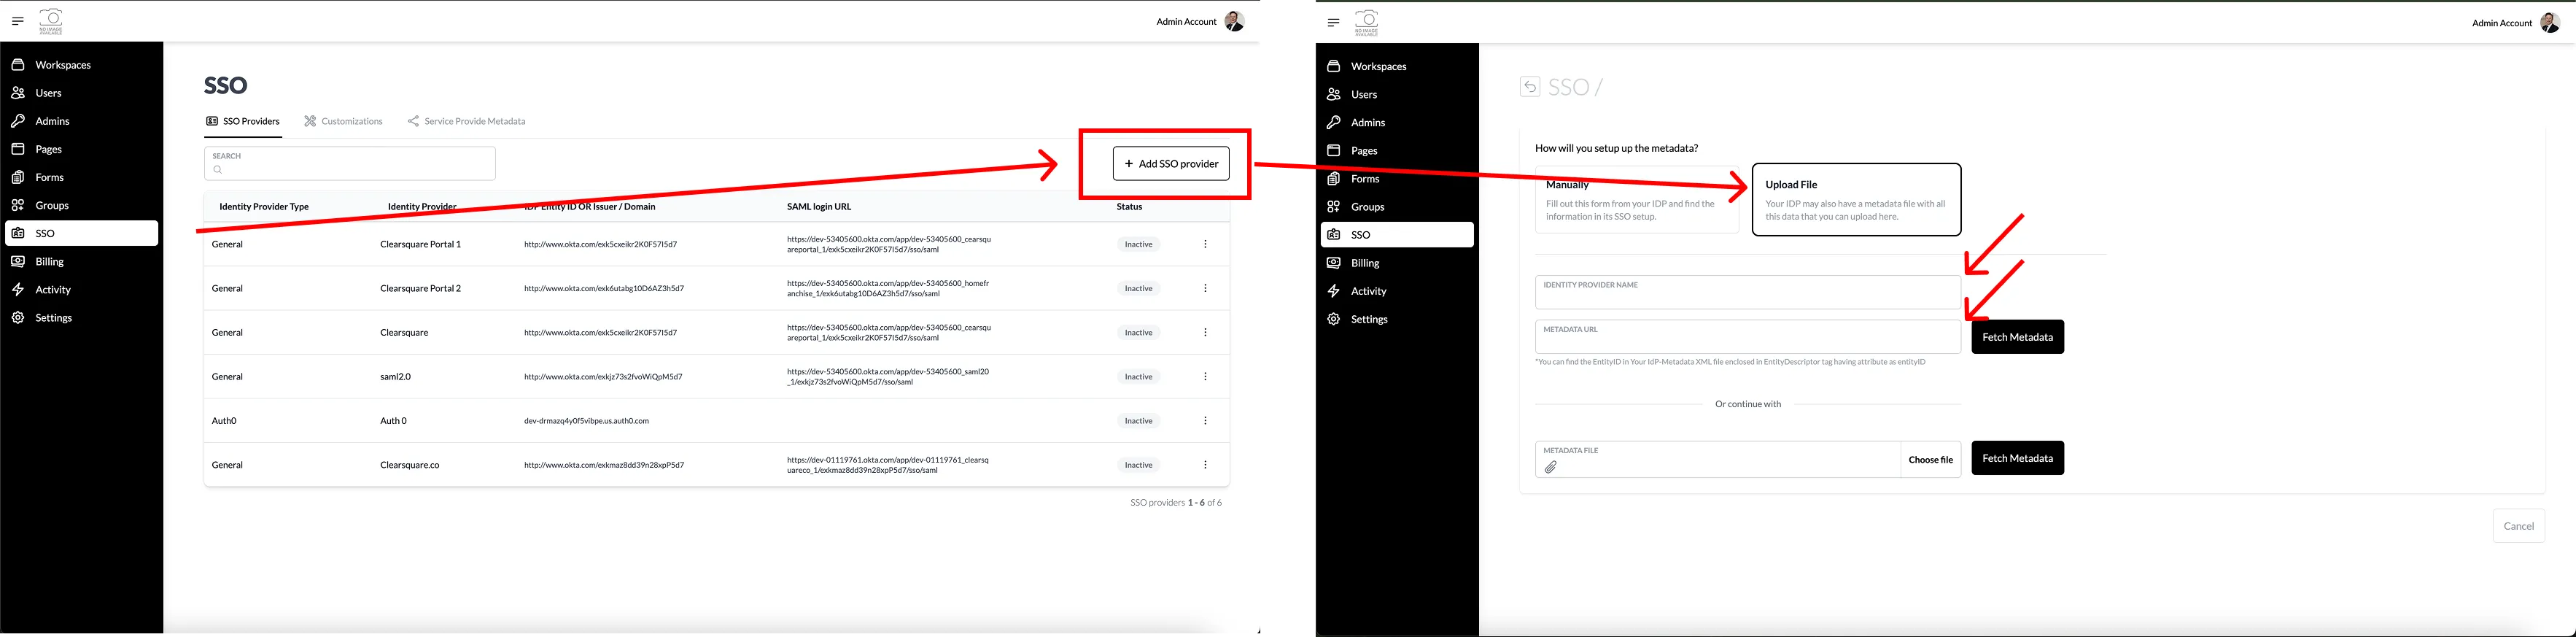
Locating the Metadata URL
Method 1: Enterprise Applications (Most Common)
- Sign in to the Microsoft Entra admin center (formerly Azure Active Directory admin center)
- Navigate to Identity > Applications > Enterprise applications
- Select your application from the list (or search for it using the search bar)
- Select Single sign-on from the left menu
- On the Set up single sign-on with SAML page, scroll down to the SAML Certificates section
- Look for App Federation Metadata Url - this is the URL you need to provide to your software provider
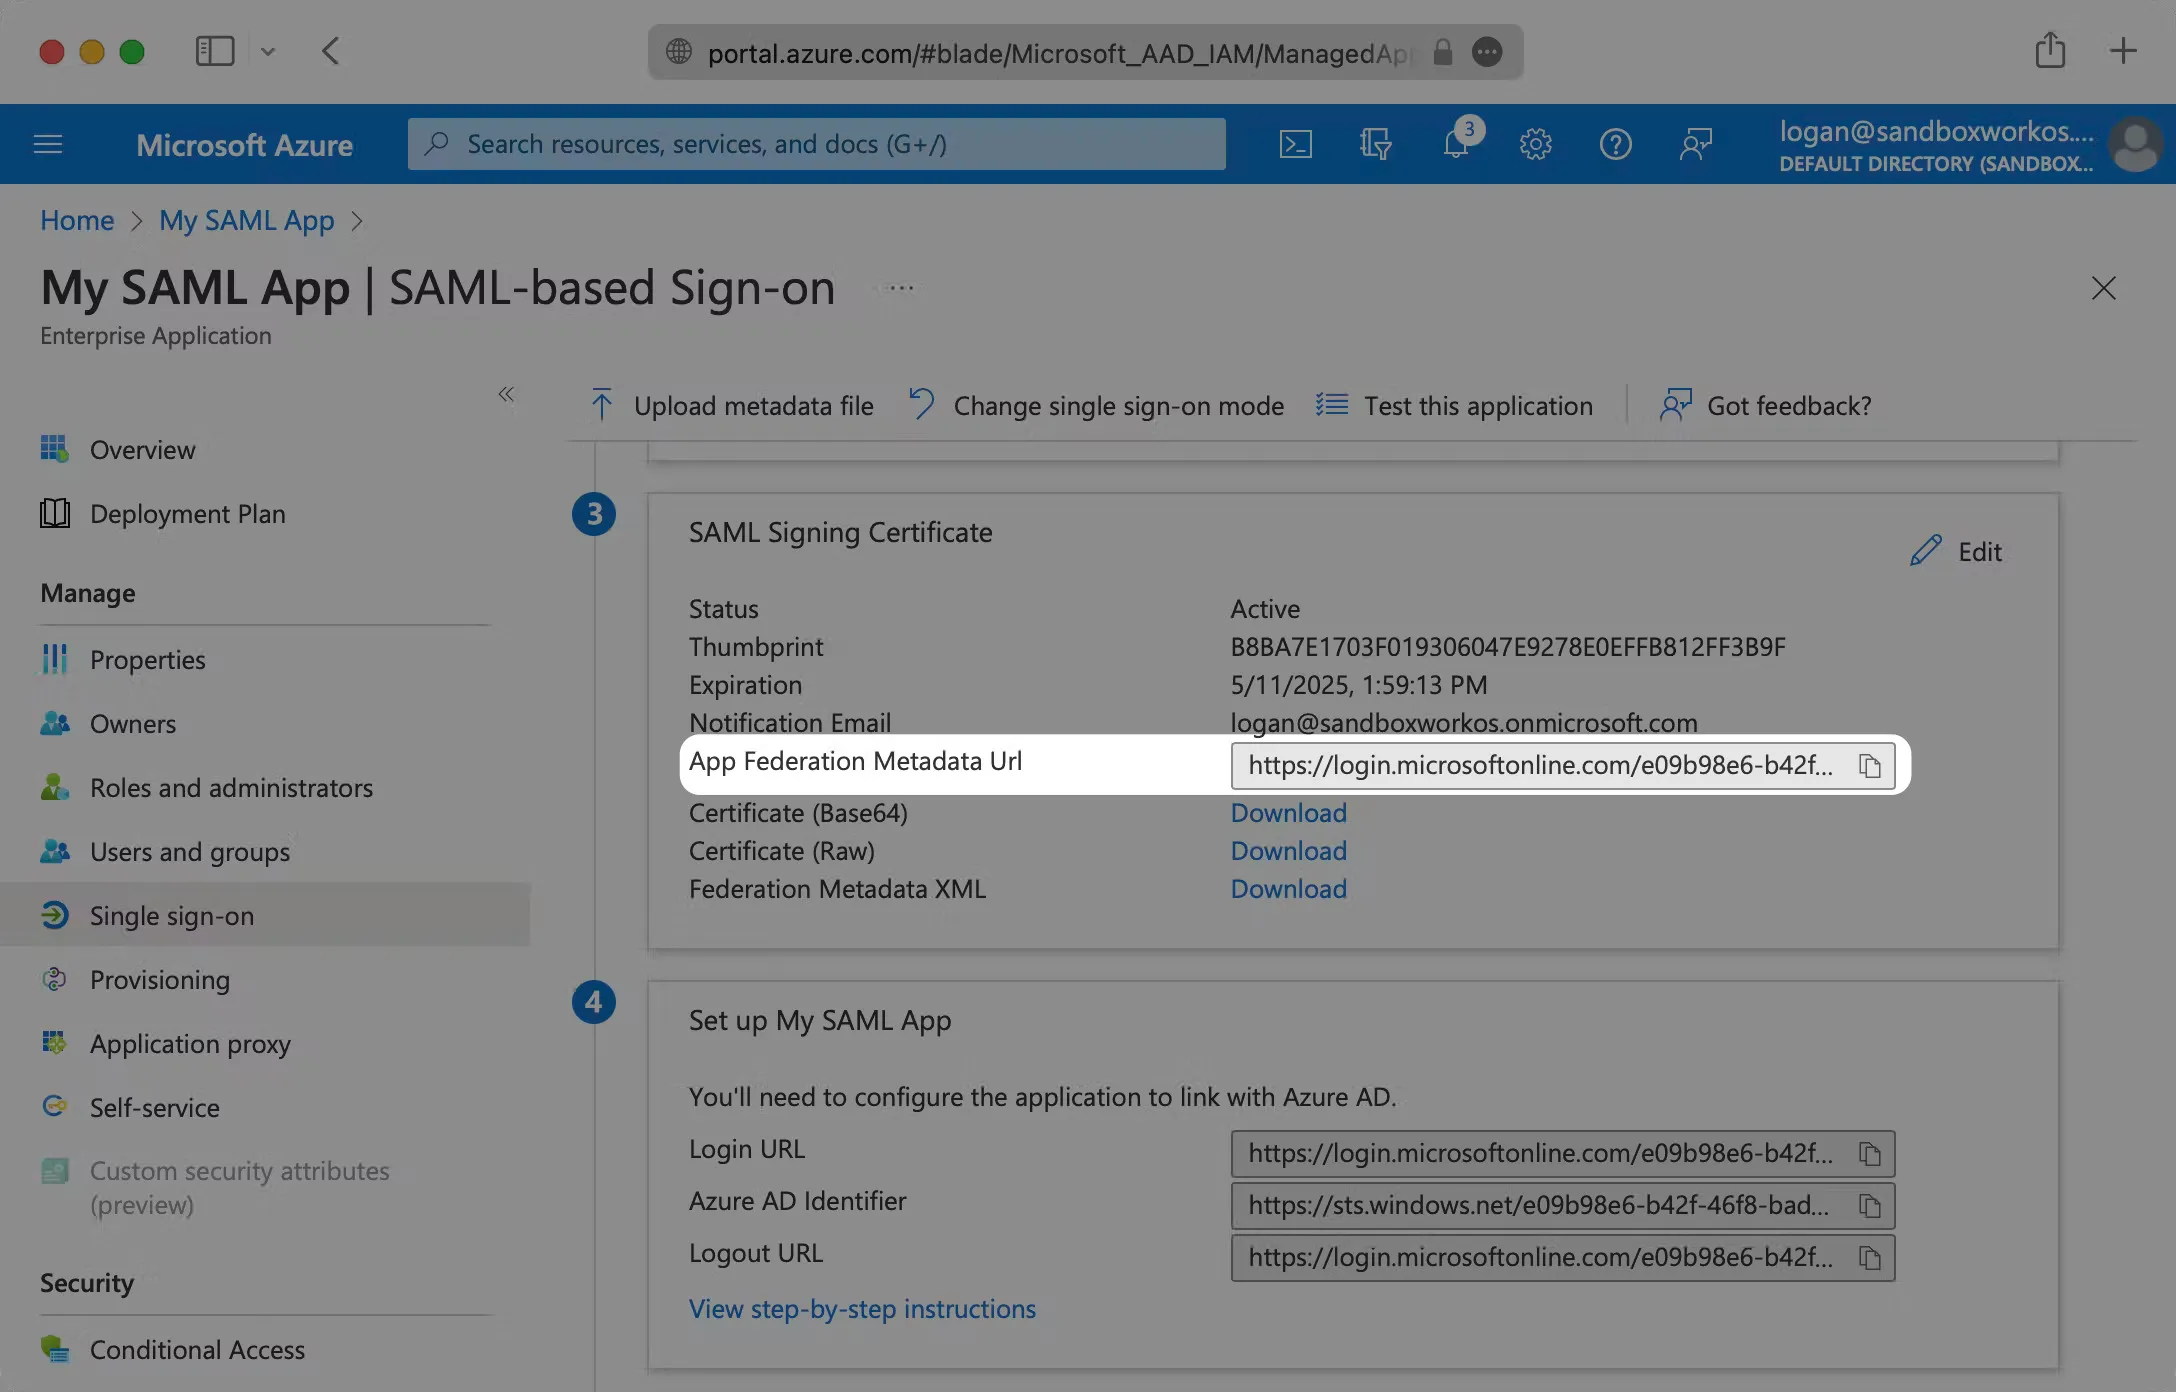
Method 2: Downloading the Federation Metadata XML
If the software vendor requires the XML file instead of the URL:
- Follow steps 1-5 from Method 1
- In the SAML Certificates section, click Download next to Federation Metadata XML
- Save this file to your computer
- Upload this file to your software provider's SSO configuration page
Method 3: Tenant-specific Federation Metadata URL
For advanced configurations, you can use the tenant-specific endpoint template:
Replace <TenantDomainName> with one of:
- Your registered domain name (e.g., contoso.onmicrosoft.com)
- Your tenant ID (a GUID)
What Information Is Shared via the Metadata URL?
The metadata URL provides the following information to your software provider:
- Identity Provider (IdP) Entity ID
- SSO endpoint URLs
- X.509 certificate for signature verification
- Attributes/claims mapping information
- Protocol support information
Next Steps
After locating and sharing the metadata URL:
- Confirm with your software provider that they received the information
- Complete any additional configuration steps required by the software
- Test the SSO configuration with a test user before rolling out to all users
- Configure user assignments in the Enterprise Application if needed
Troubleshooting
If the software provider has trouble processing the metadata URL:
- Try downloading and providing the Federation Metadata XML file instead
- Verify your application is properly configured with SAML in Azure
- Check if your software provider needs specific claim mappings configured
Note: This documentation reflects Microsoft Entra ID (formerly Azure AD) as of April 2025. Interface elements and paths may change in future Azure portal updates.